Aug 2025 – Present · India
Security Engineer Zoho Corporation
L2/L3 security engineer owning detection, endpoint, DLP, logging, vulnerability, cloud, forensics and deception operations across a 40,000+ endpoint estate. Day to day:
- CrowdStrike Falcon — full administrationSensor deployment and health, prevention & response policy configuration, host groups, and USB/device control across 40,000+ endpoints.
- Detection tuning & rule exclusionsAuthor and manage Falcon detection/prevention exclusions and custom IOAs to cut false positives without losing true-positive coverage.
- Endpoint / host firewallConfigure and maintain host-based firewall policies across the endpoint estate.
- Forcepoint DLP policy engineeringWrite and tune regex-based classifiers and DLP policies, push them to endpoints, and investigate and disposition DLP incidents to prevent data exfiltration.
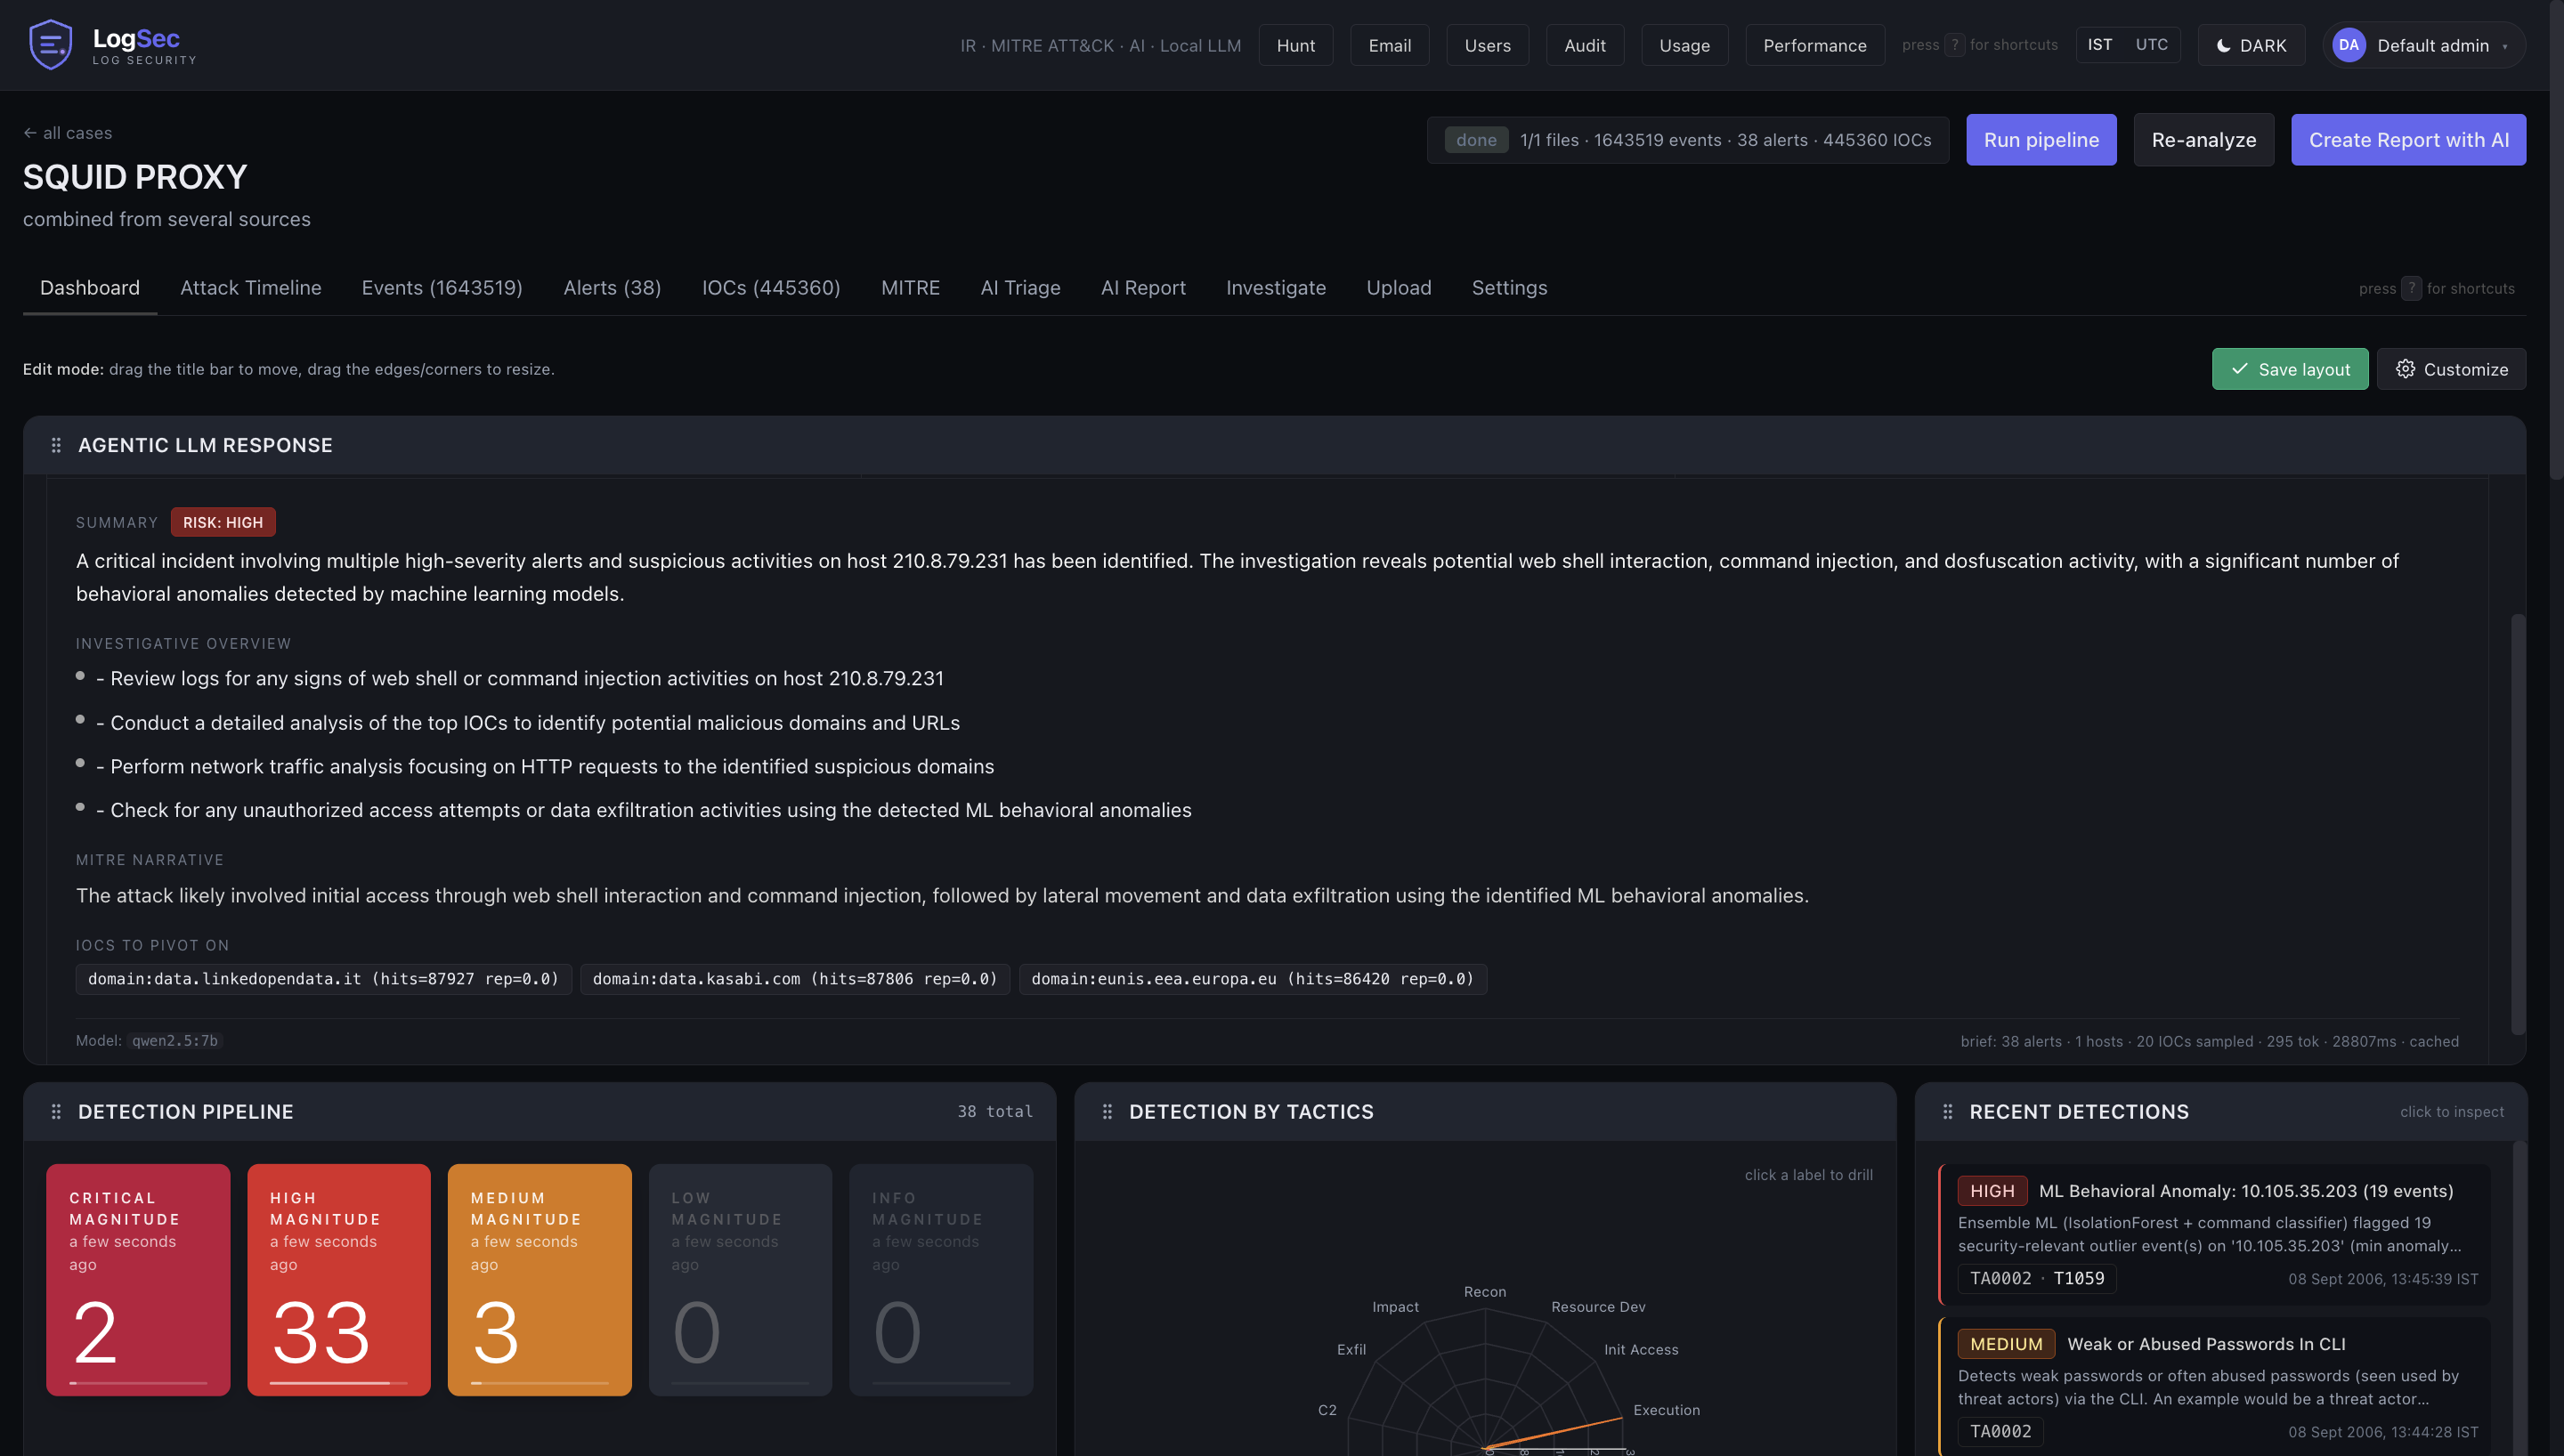
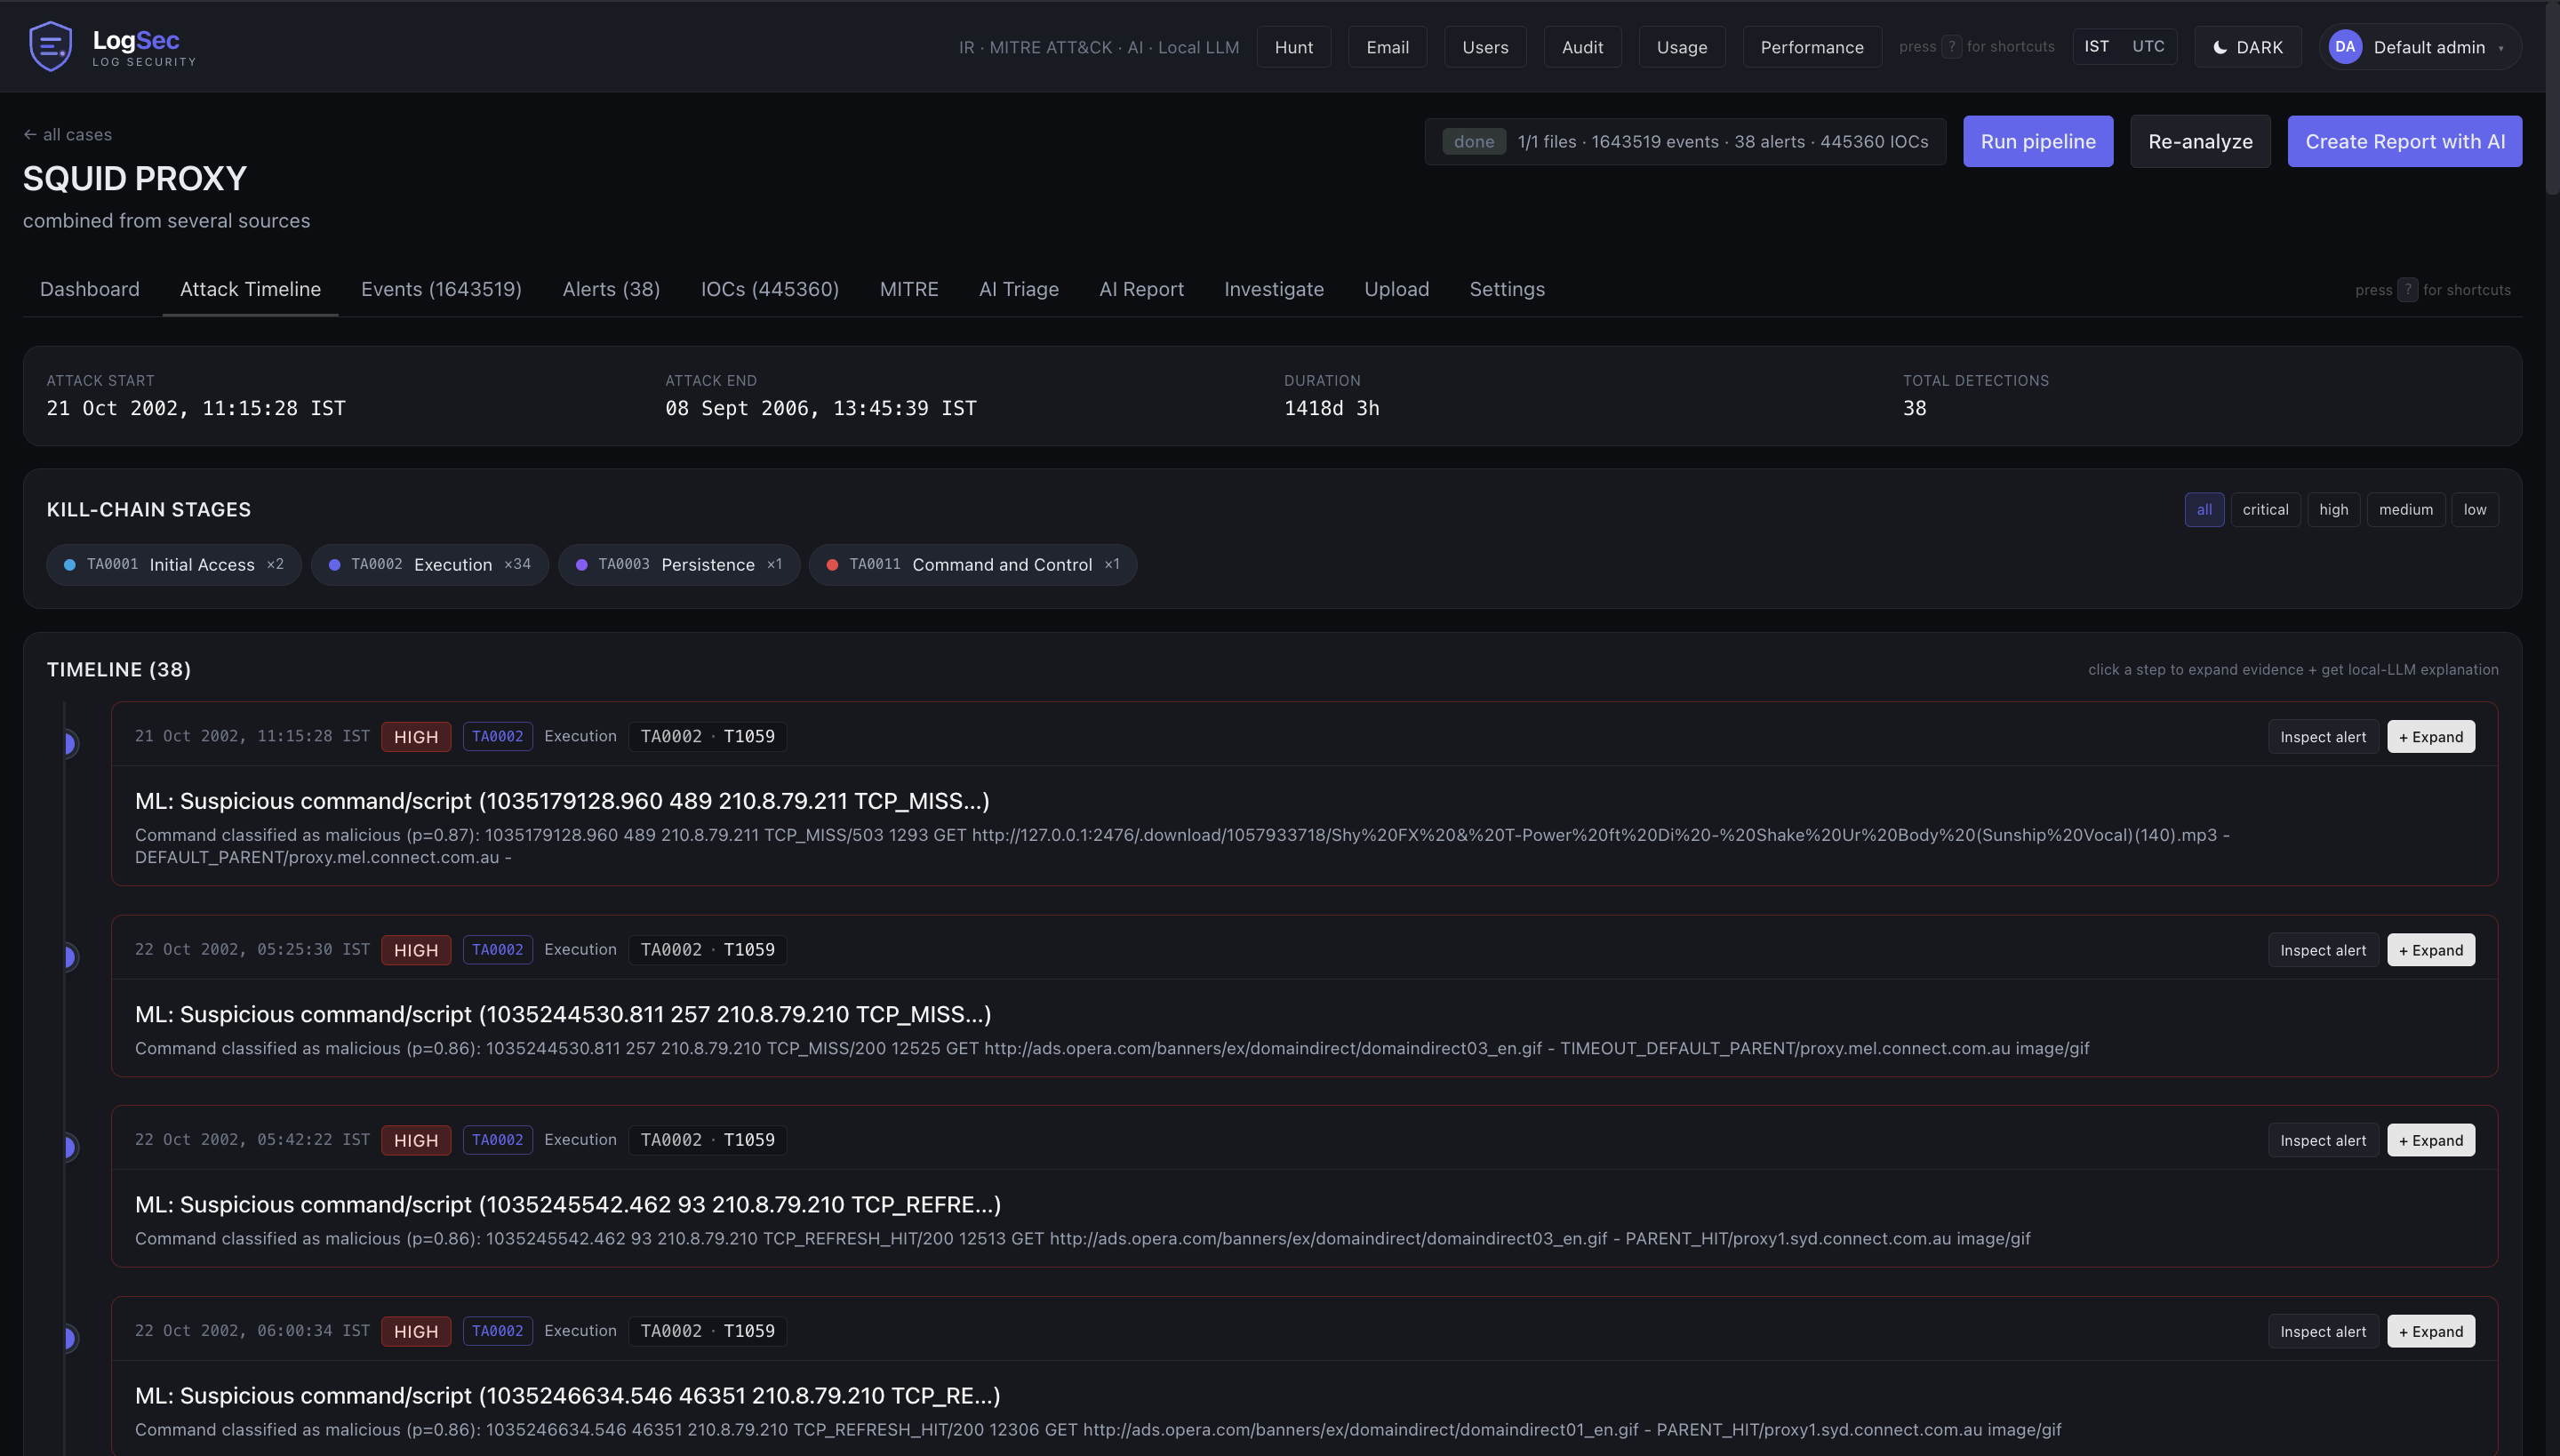
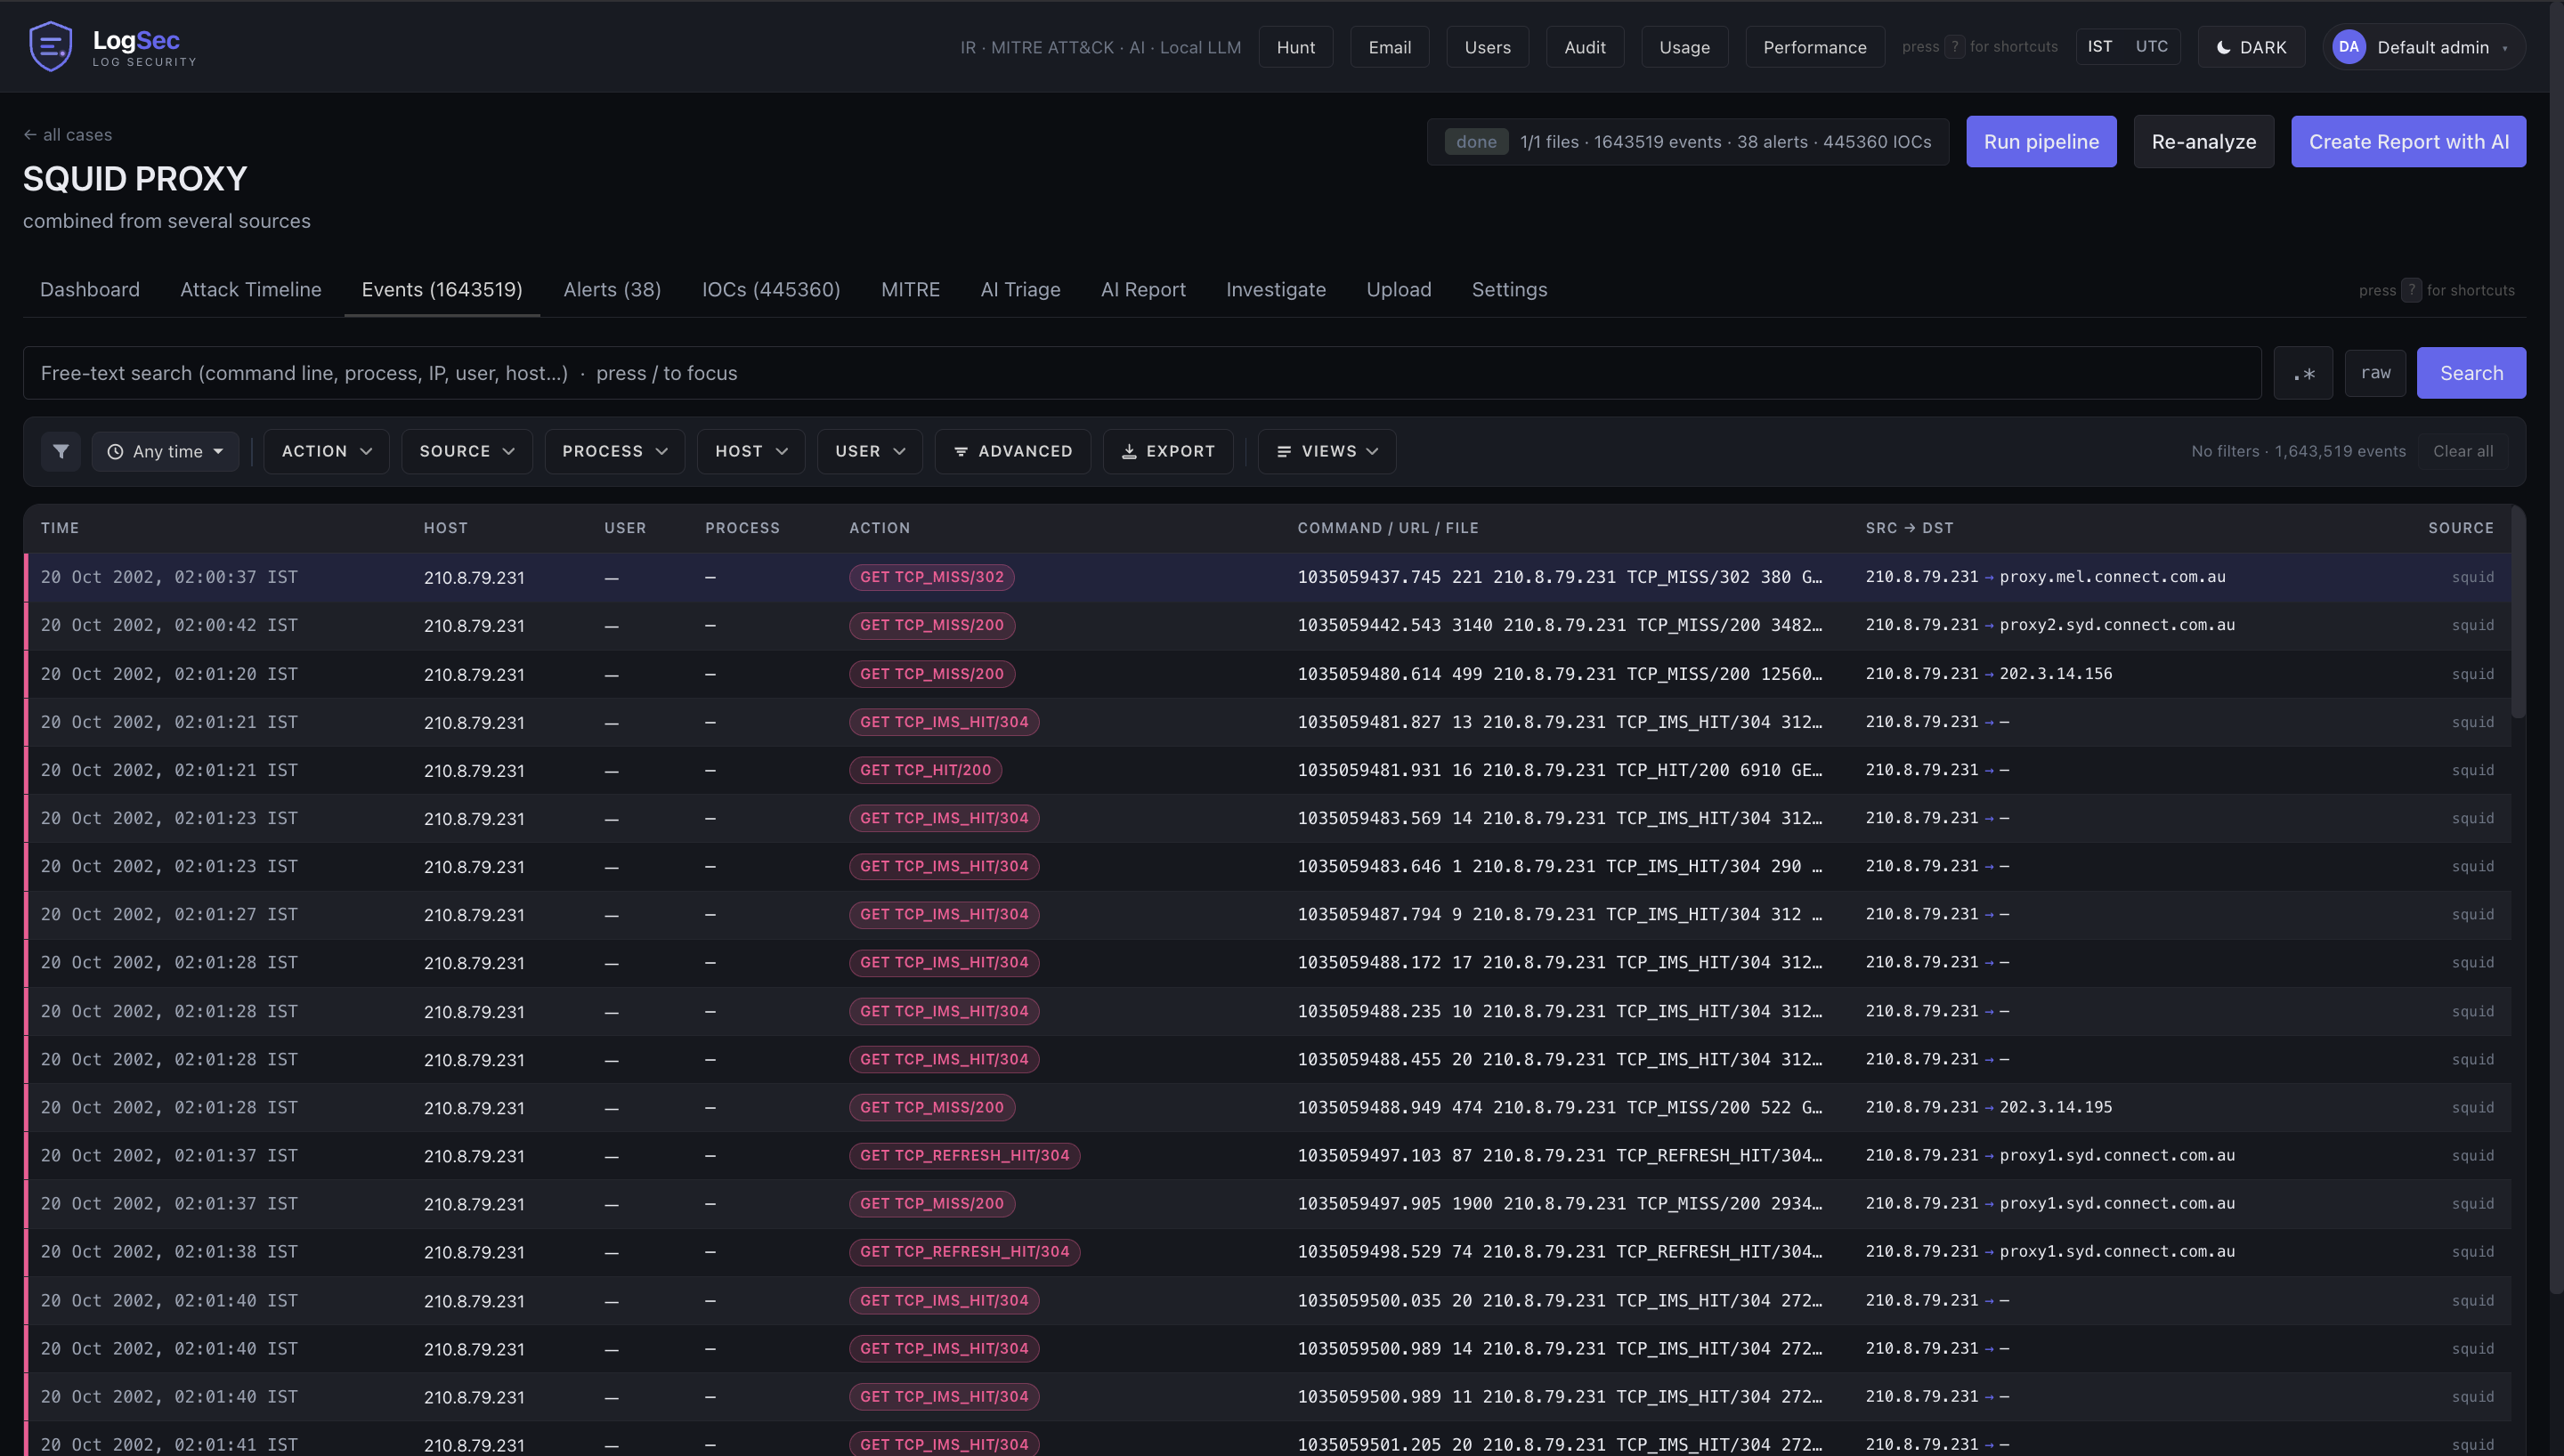
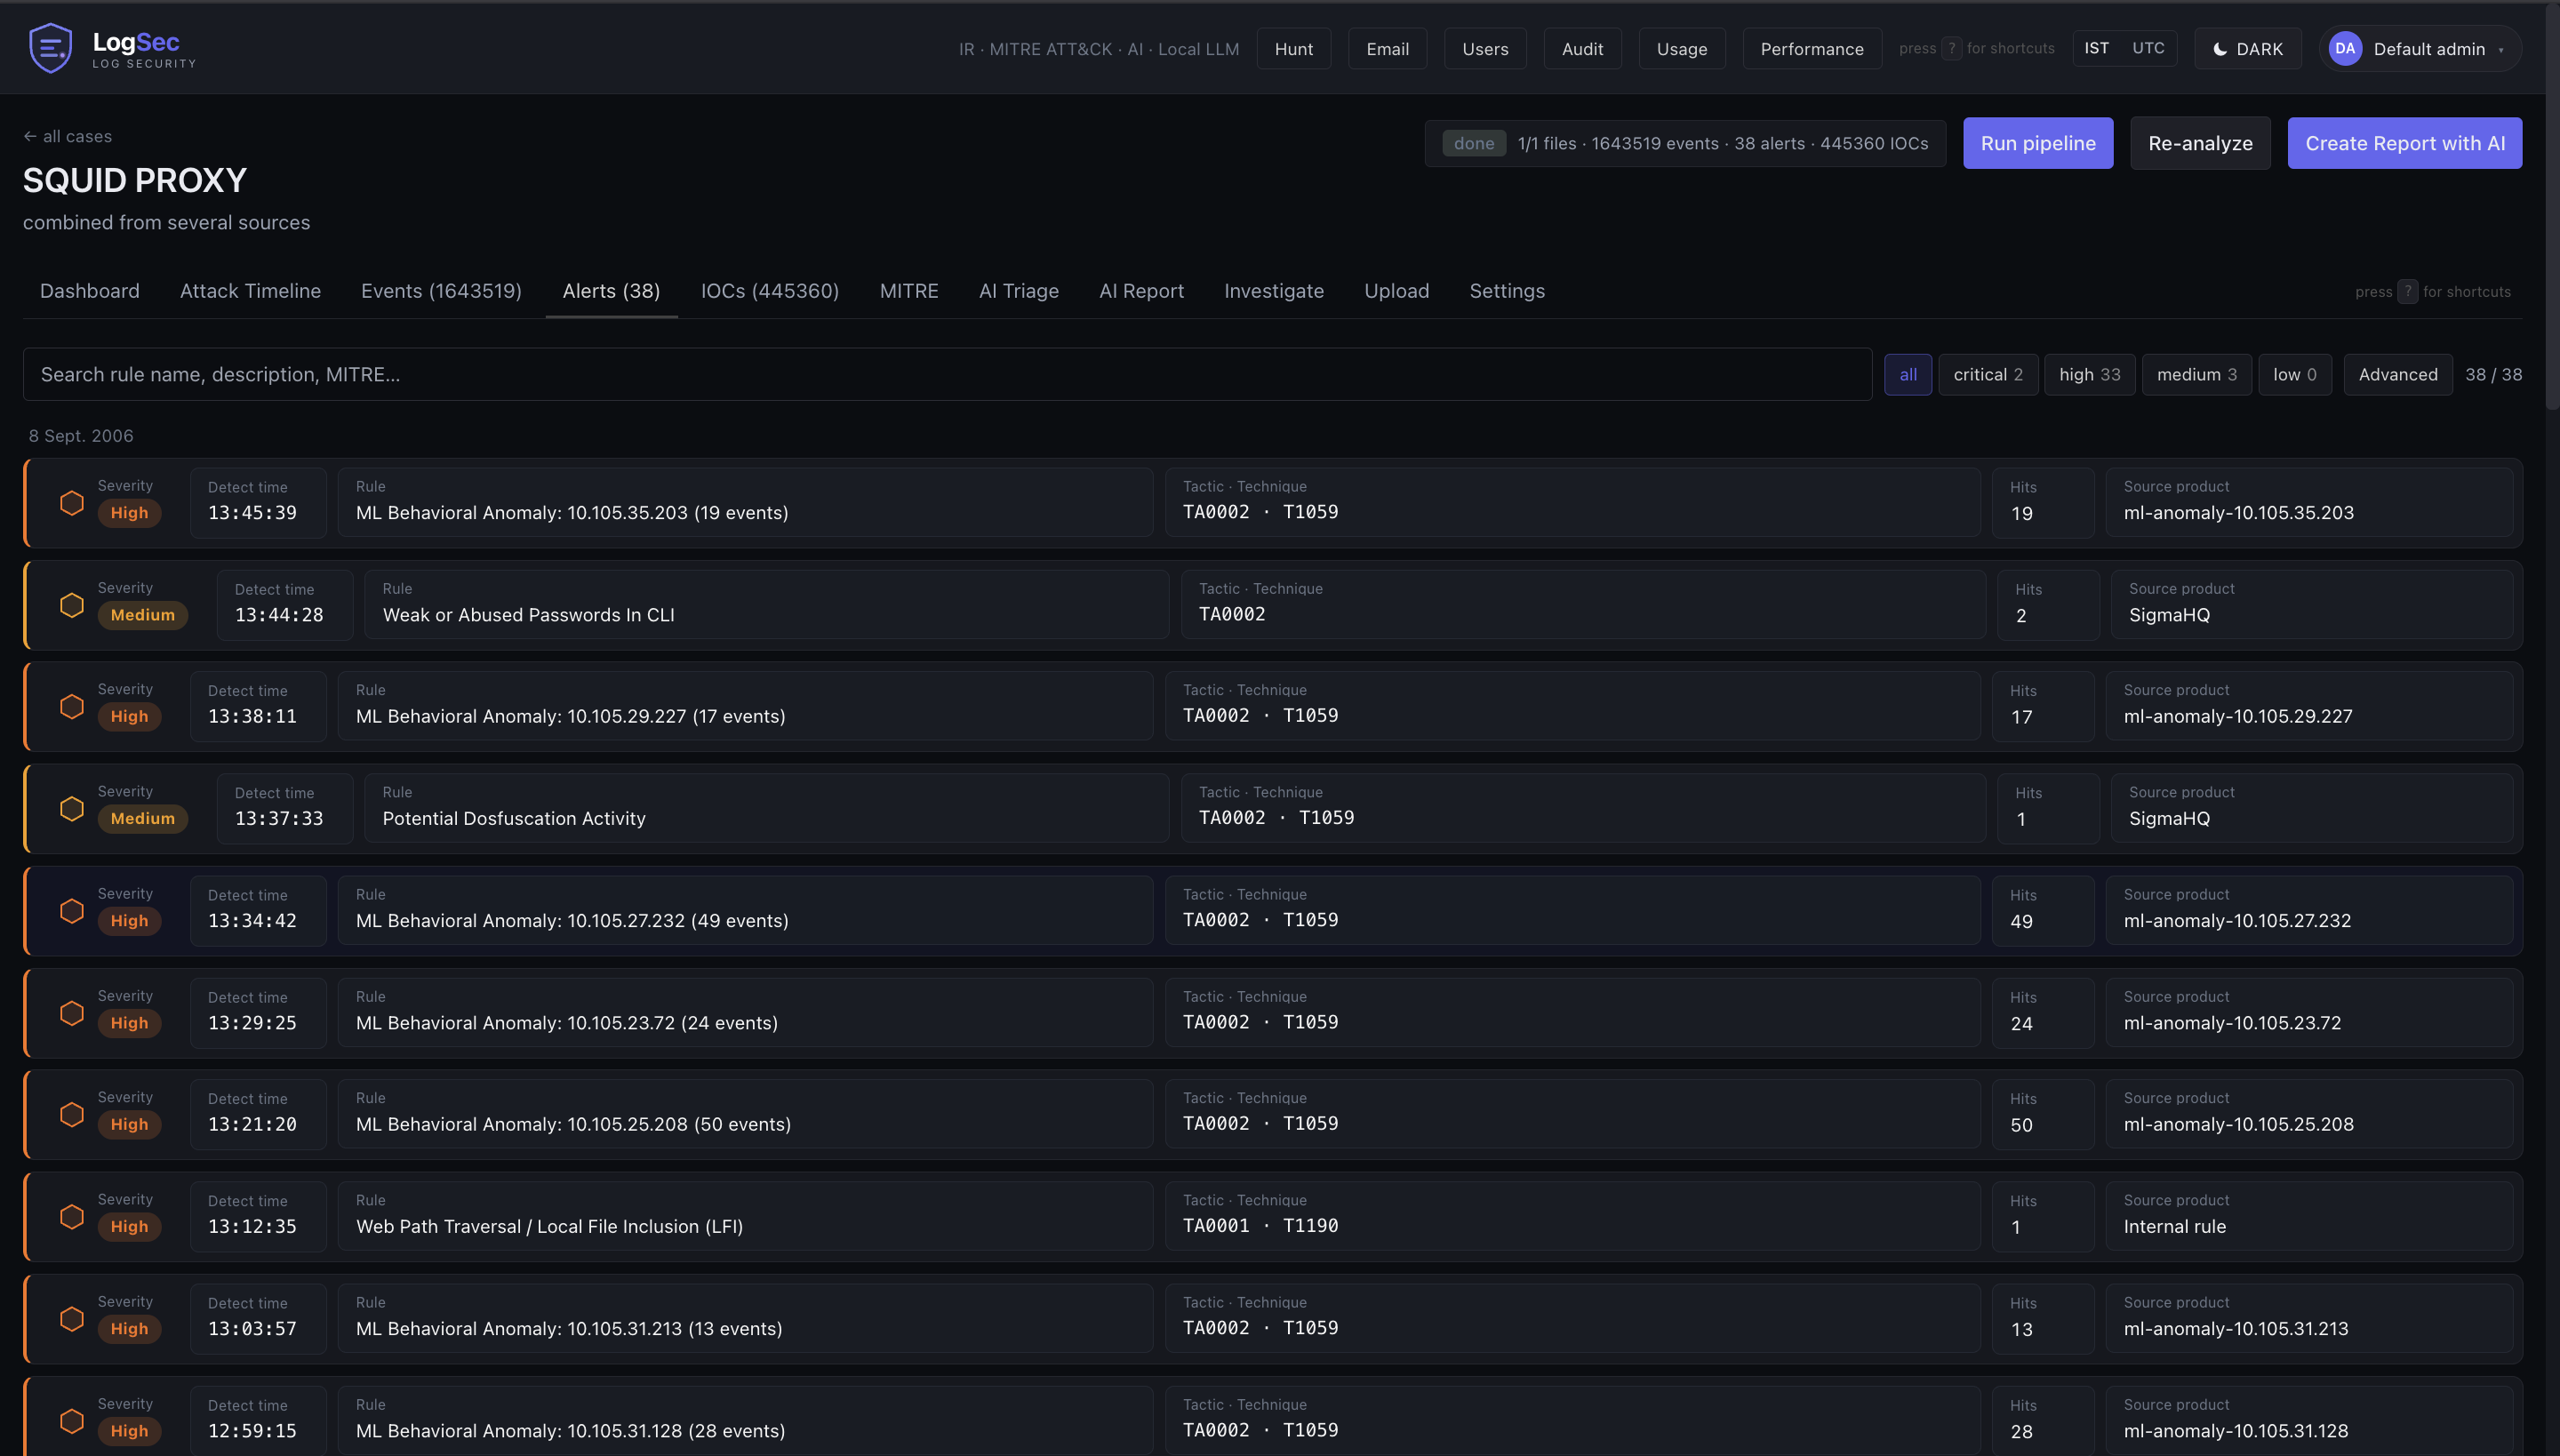
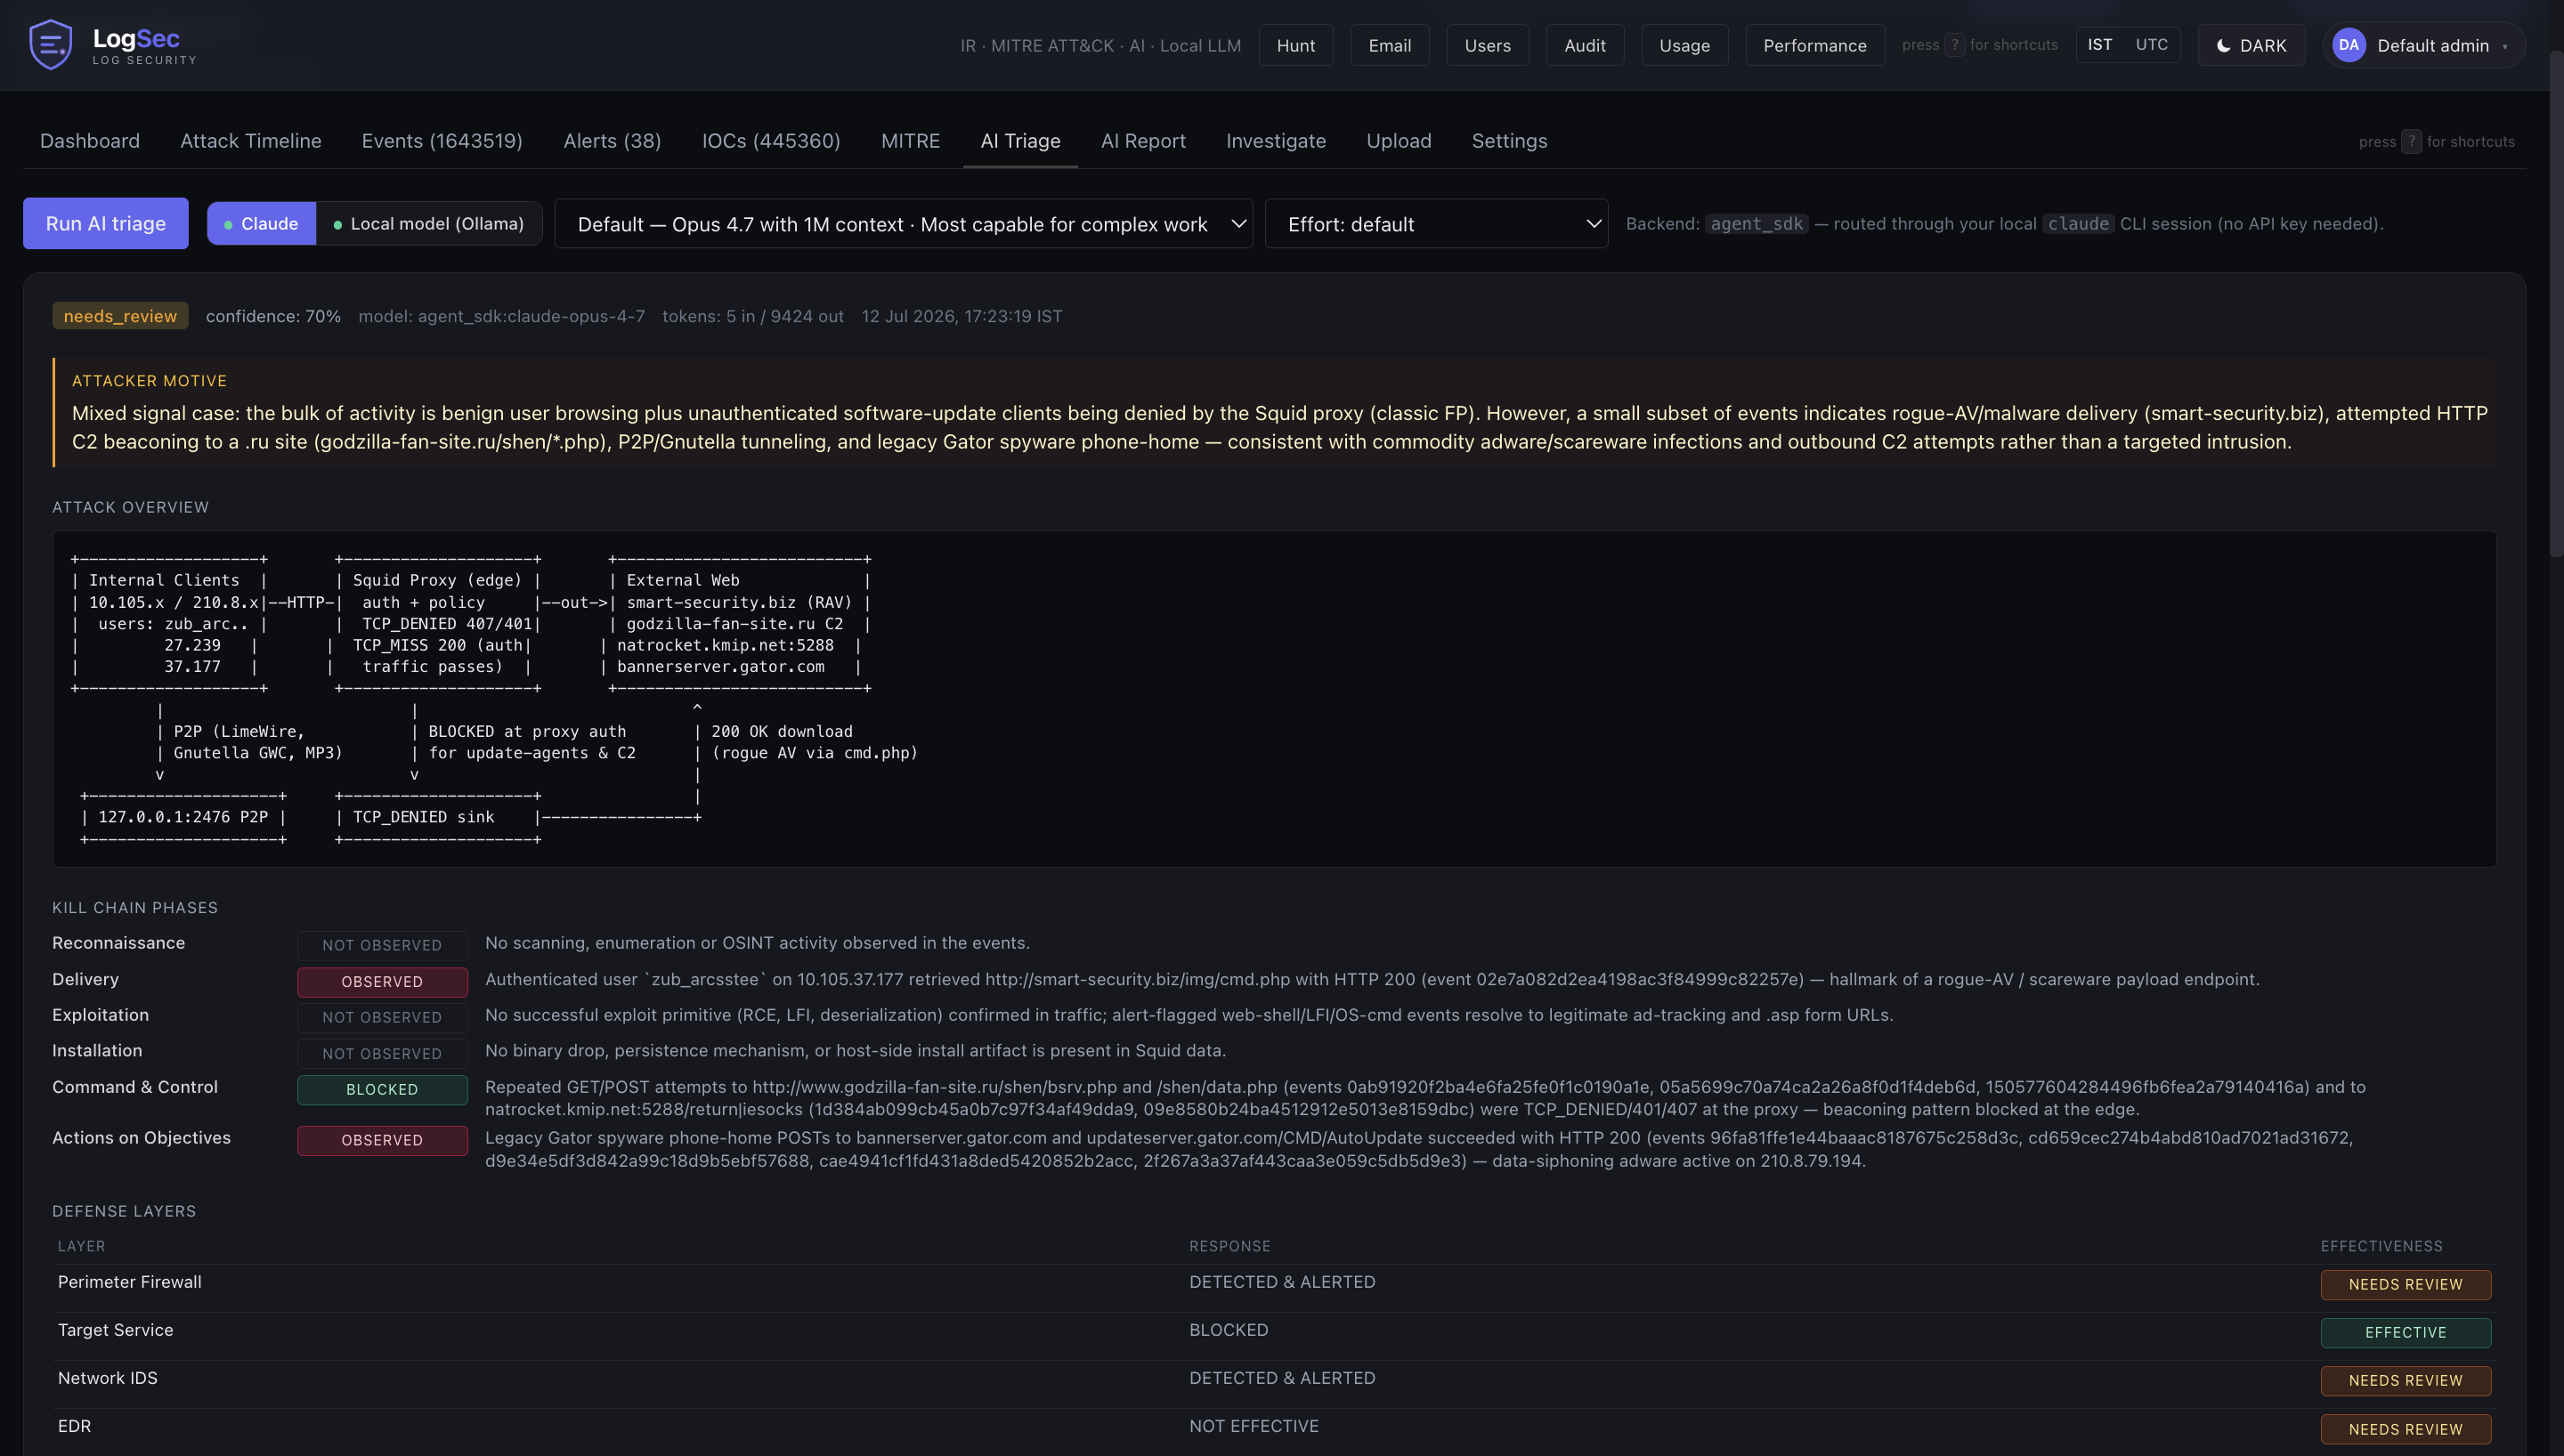
- SIEM rule engineering & log analysisBuild and fine-tune SIEM detection and correlation rules, and perform daily log analysis to hunt, validate and escalate threats.
- LogScale log-source integrationOnboard and integrate log sources into CrowdStrike Falcon LogScale (NG-SIEM), building parsers and queries to expand detection coverage.
- Cynet XDR operationsOperate Cynet XDR for cross-layer detection, correlation and response.
- Dark-web monitoringRun SpyCloud continuous monitoring for leaked corporate credentials with a triage-to-reset workflow.
- Vulnerability managementRun Nessus authenticated scanning and drive prioritized remediation to closure.
- Digital forensicsDisk and mobile image acquisition with Magnet AXIOM and Cellebrite, plus memory, disk and log analysis for investigations.
- DeceptionDeploy and monitor honeypots across multiple Zoho locations for early threat detection.
- Cloud securityMonitor and harden AWS and Azure workloads across the hybrid estate.
- Automation & toolingDevelop custom security tools and automation in Python, and implement and integrate new security tooling.
- Incident responseLead L2/L3 IR end to end — triage, containment, eradication, root-cause analysis and reporting.
CrowdStrike Falcon & LogScale · Cynet XDR · Forcepoint DLP · SpyCloud · Magnet AXIOM / Cellebrite · Nessus · AWS / Azure · Python